
Revision summary
Cyber security elements are confidentiality, integrity, availability, authentication, human process, supply chain, and legal institutions. India’s notified document is the National Cyber Security Policy 2013. A National Cyber Security Strategy was discussed around 2020; a complete public successor was not firmly in force as a single comprehensive charter by 2022. Operational bodies include CERT-In, NCIIPC and I4C, plus sector regulators. Gaps remain in MSME/hospital security, skills, supply chain and fragmented law.
Model answer
Copper italics in this answer — like this — are the key facts. Each one is unpacked in the Facts & figures rail.
Introduction
Cyber security is the protection of networks, devices, data and people from unauthorised access and disruption. It is not only a firewall. India has a National Cyber Security Policy, 2013, a CERT-In, sectoral CERTs, and years of discussion of a fuller National Cyber Security Strategy (a public draft conversation around 2020). Comprehensive on paper is not the same as comprehensive in every ministry and firm.
Body
Elements of cyber security
- Confidentiality: secrets and personal data stay with those allowed (encryption, access control). The Digital Personal Data Protection trajectory later added a legal overlay; in 2022 the IT Act and SPDI rules were still the main personal-data peg.
- Integrity: data and software are not silently altered (hashing, signing, secure updates).
- Availability: systems stay up under attack (DDoS defence, backups, redundancy)—critical for power, payments and hospitals.
- Authentication and identity: who is at the keyboard; Aadhaar and e-sign help citizens but also enlarge the target.
- People and process: phishing is still the usual door; training, least privilege, and incident response matter as much as tools.
- Physical and supply chain: devices, undersea cables, and hardware/software provenance.
- Legal-institutional: offences, MLATs, CERT-In directions, and sector regulators (RBI for banks, CERT-In for incident reporting).
- Offensive-defensive balance: attribution, critical-information-infrastructure protection under the NCIIPC, and military cyber commands as a separate but related layer.
How far a comprehensive National Cyber Security Strategy?
- 2013 Policy: the notified National Cyber Security Policy set aims—secure computing, 24×7 CERT-In, manpower, and public–private partnership. It was a policy, light on dated targets, budgets and ministry-by-ministry duties.
- 2020 discussion: the National Security Council Secretariat process and a draft National Cyber Security Strategy around 2020 sought to update 2013 for 5G, cloud, supply chain, and a whole-of-nation approach. A single, fully notified, publicly detailed successor strategy was still awaited / partial in public domain at the time of the 2022 paper—candidates should not invent a gazette date that did not exist.
- What does exist in practice: CERT-In (including 2022-type incident-reporting directions), NCIIPC for critical infrastructure, I4C (Indian Cyber Crime Coordination Centre), State cyber police, National Critical Information Infrastructure notifications, RBI/SEBI/IRDAI circulars, and Defence cyber capacity.
- Gaps versus ‘comprehensive’: uneven State capacity; MSME and hospital security; supply-chain assurance for telecom; shortage of skilled analysts; fragmented laws (IT Act 2000 amendments vs a dedicated cyber security statute); and the tension between CERT-In logging directions and privacy/startup cost.
- Verdict: India has a policy (2013) plus a dense operational stack, and a strategy still more discussed than finally, fully public as one binding 2020 text. It is substantial but not yet one comprehensive, uniformly implemented national strategy.
What would make it comprehensive
- One public strategy with roles, funds, and review dates; cyber hygiene for MSMEs; supply-chain rules; and judicial capacity—without treating every citizen log as a security win.
Flow diagram
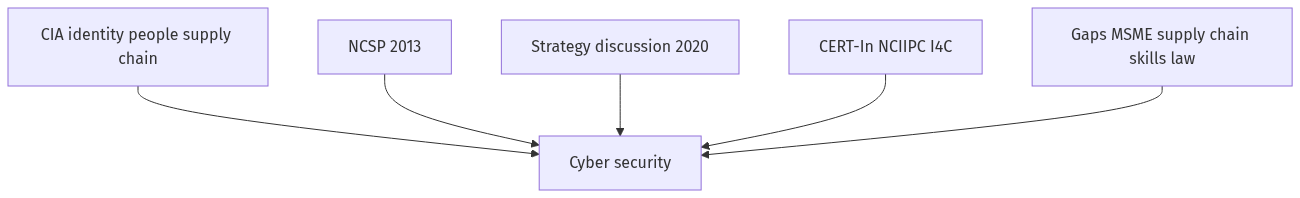
Conclusion
Cyber security is confidentiality, integrity, availability, identity, people, supply chain and law. India notified a 2013 policy and built CERT-In, NCIIPC and I4C. A full National Cyber Security Strategy was under discussion around 2020 and was not yet a complete, uniformly applied public charter by the 2022 exam window. The stack is real; the single strategy is unfinished.
Quick related
Students also ask
-
Discuss how emerging technologies and globalisation contribute to money laundering. Elaborate measures to tackle the problem of money laundering both at national and international levels.
Next question on this syllabus topic (2021 · Q9). View answer →
-
Is the 2013 document a ‘strategy’?
It is a policy. A strategy usually adds threats, resources, timelines and roles. That fuller NCSS text was still in process around 2020.
-
Does CERT-In equal comprehensive national cyber security?
CERT-In is the incident node. Comprehensive security also needs NCIIPC, police, regulators, firms and users.
Same topic · past papers
UPSC has asked this before
These previous-year questions sit on the same topic. Open one to practise the earlier ask.
More from this topic
Q20 · UPSC Mains 2026 · GS III · 15 marks · Solution
Discuss counterfeit currency and money laundering as major sources of terror funding in India. State the actions being taken at International level to check these menaces. Highlight the role of Financial Action Task Force (FATF) and methods of compliance by its member states in preventing terror funding.
Cyber Security and Money Laundering
• FICN funds networks and damages monetary trust. • Laundering uses placement–layering–integration, hawala and sometimes digital rails. • India: PMLA, UAPA finance provisions, FIU-IND, ED, NIA, RBI AML/KYC. • International: UN terror-finance conventions and sanctions lists. • FATF sets global AML/CFT standards via 40 Recommendations. • Members comply through laws, FIUs, KYC/STR duties, beneficial ownership, freezes. • Mutual evaluations judge both technical rules and real-world effectiveness. • Grey/black listing raises correspondent-banking and reputational costs.
Q9 · UPSC Mains 2026 · GS III · 10 marks · Solution
Explain how fake news and disinformation pose threat to Internal Security and Public Order in Indian context? In this regard, discuss salient features of amendments in respect of Information Technology (Intermediatory Guidelines and Digital Media Ethics Code) Rules 2021.
Cyber Security and Money Laundering
• Viral falsehoods can trigger communal violence and mob justice. • Disinformation aids radicalisation and confuses crisis response. • Elections and institutional trust are soft targets of coordinated lies. • IT Rules 2021 impose due diligence and grievance duties on intermediaries. • April 2023 amendment added government FCU flagging for Centre-related falsehoods. • PIB Fact Check Unit notified 20 March 2024 under the Rules. • Bombay HC (Sep 2024) struck down the FCU amendment as unconstitutional; further litigation ongoing. • Lasting response needs literacy, fast official facts, and proportionate law.
Q10 · UPSC Mains 2021 · GS III · 10 marks · Solution
Keeping in view India's internal security, analyse the impact of cross-border cyber attacks. Also discuss defensive measures against these sophisticated attacks.
Cyber Security and Money Laundering
Cross-border cyber operations can stall critical infrastructure, rob finance, and steal state data without a kinetic raid. Attribution problems let states and proxies hide behind criminal malware. CERT-In, NCIIPC, Defence Cyber Agency, sector CERTs, and the IT Act are the Indian defensive core. Segmentation, backups, vendor control, and phishing defence are the practical layer. Resilience and international CERT cooperation matter more than a claim of perfect security.