
Revision summary
Cross-border cyber operations can stall critical infrastructure, rob finance, and steal state data without a kinetic raid. Attribution problems let states and proxies hide behind criminal malware. CERT-In, NCIIPC, Defence Cyber Agency, sector CERTs, and the IT Act are the Indian defensive core. Segmentation, backups, vendor control, and phishing defence are the practical layer. Resilience and international CERT cooperation matter more than a claim of perfect security.
Model answer
Copper italics in this answer — like this — are the key facts. Each one is unpacked in the Facts & figures rail.
Introduction
Cross-border cyber attacks are a cheap way for a rival state, a proxy, or a criminal gang abroad to hit Indian banks, power, railways, and public trust without a visible soldier. For internal security they sit beside terrorism and subversion: the border is a router, not only a fence.
Body
Impact on internal security
- Critical infrastructure — power grids, ports, railways, oil, and telecom — can be slowed or blinded, which creates urban disorder without an explosion.
- Banks, UPI rails, and markets face theft, ransomware, and loss of confidence, which is a domestic stability problem as much as a cyber-crime problem.
- Attribution is slow. A server in a third country can mask a state or a non-state actor, which complicates response under international law.
- Espionage and influence: theft of defence and ministry data, and information operations that inflame communal or separatist fault lines.
- Terror and insurgent use: encrypted command, funding, and targeting of police databases. The 2020s pattern is mixed criminal–state toolkits (supply-chain malware, zero-days).
- Examples in the public domain include probes and incidents around Kudankulam (2019 reporting), Mumbai power disturbance debates in 2020, and repeated Chinese and Pakistan-linked campaign reporting by CERT-In and private firms. Exact operational detail is often classified; the strategic fact is persistent targeting.
Defensive measures
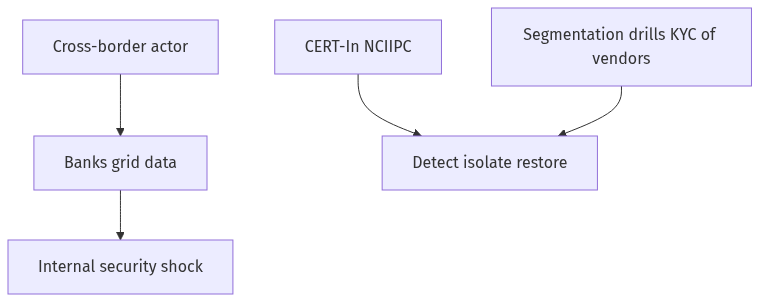
- CERT-In as the national incident response node; NCIIPC for designated critical information infrastructure under the IT Act.
- Network monitoring, segmentation, backups, and air-gapping of the most sensitive control systems; no internet-facing SCADA by default.
- Defence Cyber Agency and service cyber commands for military networks; NATGRID and police cyber cells for the criminal layer.
- IT Act offences, data-protection rules as they evolve, sector CERT (finance, power), and mandatory incident reporting.
- Supply-chain hygiene: trusted telecom gear, software bills of materials, and audits of vendors.
- International: Budapest Convention cooperation even without full membership politics, bilateral CERT MoUs, and UN norms on not attacking critical civilian infra.
- People: phishing is still the main door. Training, zero-trust identity, and public–private drills matter more than a new logo.
Limits
- Perfect defence is false. The aim is resilience: detect, isolate, restore, and attribute well enough to deter.
Flow diagram
Conclusion
Cross-border cyber attacks threaten Indian internal security by hitting money, power, data, and social trust from outside the fence. Defence is CERT-In, NCIIPC, segmented critical systems, cyber commands, and drills — resilience, not an unbreakable wall.
Quick related
Students also ask
-
Discuss different types of cybercrimes and measures required to be taken to fight the menace.
Next question on this syllabus topic (2020 · Q9). View answer →
-
Is every ransomware attack an act of war?
No. Many are criminal. Some use state tools. Internal security response starts with incident handling, then attribution.
-
Can India air-gap everything?
Not banks and railways that must talk to the world. Air-gap the control core; monitor the rest; practise restore.
Same topic · past papers
UPSC has asked this before
These previous-year questions sit on the same topic. Open one to practise the earlier ask.
-
2019 · Q20 · GS III · 15 marks
Cross-Border movement of insurgents is only one of the several security challenges facing the policing of the border in North-East India. Examine the various challenges currently emanating across the India-Myanmar border. Also, discuss the steps to counter the challenges.
More from this topic
Q20 · UPSC Mains 2026 · GS III · 15 marks · Solution
Discuss counterfeit currency and money laundering as major sources of terror funding in India. State the actions being taken at International level to check these menaces. Highlight the role of Financial Action Task Force (FATF) and methods of compliance by its member states in preventing terror funding.
Cyber Security and Money Laundering
• FICN funds networks and damages monetary trust. • Laundering uses placement–layering–integration, hawala and sometimes digital rails. • India: PMLA, UAPA finance provisions, FIU-IND, ED, NIA, RBI AML/KYC. • International: UN terror-finance conventions and sanctions lists. • FATF sets global AML/CFT standards via 40 Recommendations. • Members comply through laws, FIUs, KYC/STR duties, beneficial ownership, freezes. • Mutual evaluations judge both technical rules and real-world effectiveness. • Grey/black listing raises correspondent-banking and reputational costs.
Q9 · UPSC Mains 2026 · GS III · 10 marks · Solution
Explain how fake news and disinformation pose threat to Internal Security and Public Order in Indian context? In this regard, discuss salient features of amendments in respect of Information Technology (Intermediatory Guidelines and Digital Media Ethics Code) Rules 2021.
Cyber Security and Money Laundering
• Viral falsehoods can trigger communal violence and mob justice. • Disinformation aids radicalisation and confuses crisis response. • Elections and institutional trust are soft targets of coordinated lies. • IT Rules 2021 impose due diligence and grievance duties on intermediaries. • April 2023 amendment added government FCU flagging for Centre-related falsehoods. • PIB Fact Check Unit notified 20 March 2024 under the Rules. • Bombay HC (Sep 2024) struck down the FCU amendment as unconstitutional; further litigation ongoing. • Lasting response needs literacy, fast official facts, and proportionate law.
Q19 · UPSC Mains 2022 · GS III · 15 marks · Solution
What are the different elements of cyber security ? Keeping in view the challenges in cyber security, examine the extent to which India has successfully developed a comprehensive National Cyber Security Strategy.
Cyber Security and Money Laundering
Cyber security elements are confidentiality, integrity, availability, authentication, human process, supply chain, and legal institutions. India’s notified document is the National Cyber Security Policy 2013. A National Cyber Security Strategy was discussed around 2020; a complete public successor was not firmly in force as a single comprehensive charter by 2022. Operational bodies include CERT-In, NCIIPC and I4C, plus sector regulators. Gaps remain in MSME/hospital security, skills, supply chain and fragmented law.