
Revision summary
Cybercrime targets persons, money, computers, and critical infrastructure, often in mixed form. Phishing, UPI fraud, ransomware, CSAM, and CII attacks are the live Indian set. IT Act plus ordinary criminal law, CERT-In, NCIIPC, I4C, and RBI rules are the state toolkit. Backups, MFA, platform duty, and forensic capacity are the practical layer. Most retail cases are social engineering, so literacy is a security control.
Model answer
Copper italics in this answer — like this — are the key facts. Each one is unpacked in the Facts & figures rail.
Introduction
Cybercrime is offence in which a computer or a network is the target, the tool, or the scene of evidence. In India it rides cheap smartphones, UPI, and social media. Types differ; the fight has to mix criminal law, CERT-In, banks, and public habit — not only a new section in the IT Act.
Body
Types
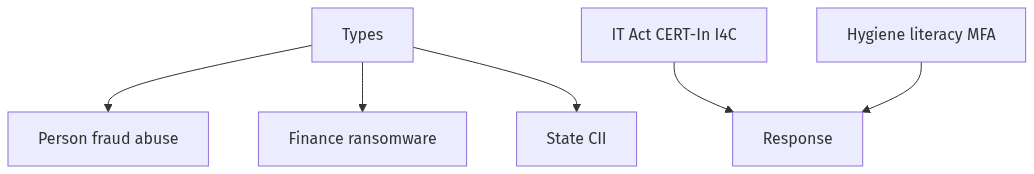
- Against persons: phishing, SIM-swap, OTP fraud, sextortion, cyberstalking, morphing, and child sexual-abuse material online.
- Against property and finance: ransomware, business-email compromise, credit-card and UPI fraud, crypto-enabled laundering, and theft of intellectual property.
- Against the State and infrastructure: website defacement, DDoS, espionage, attacks on CII (power, finance, telecom), and information operations.
- Against computers themselves: malware, botnets, supply-chain compromise.
- Intermediary-enabled harms: fake news for riot, terror recruitment, and drug or arms markets on encrypted apps — crime that is social but cyber-delivered.
Legal and institutional measures
- IT Act, 2000 (with 2008 amendments): unauthorised access, data theft, impersonation, child pornography provisions; IPC/BNS for cheating, defamation, sexual offences that merely use a phone.
- Indian Computer Emergency Response Team (CERT-In) for incident response and directions; NCIIPC for designated critical information infrastructure.
- Police cyber cells, the I4C (Indian Cyber Crime Coordination Centre), and the national cybercrime reporting portal.
- RBI and NPCI rules for payment fraud, two-factor authentication, and bank liability frameworks.
- International: MLATs, Interpol, and cooperation even where India is cautious about the Budapest Convention’s politics.
Technical and social measures
- Hygiene: updates, MFA, segmented networks, backups against ransomware, and no internet-facing SCADA.
- Platform duty: faster takedown of CSAM and fraud pages; KYC on wallets; audit of large intermediaries.
- Literacy: most retail crime is social engineering. School and bank campaigns matter more than a new firewall logo.
- Capacity: trained magistrates and forensic labs so Section 65B evidence actually convicts.
- Supply chain: trusted telecom gear and software bills of materials for government and CII.
Flow diagram
Conclusion
Cybercrime ranges from OTP theft to ransomware on a grid. Fighting it needs the IT Act and IPC together, CERT-In and I4C, payment-system rules, and a public that does not type an OTP to a stranger. Technology without investigation and literacy will not close the menace.
Quick related
Students also ask
-
What is CyberDome Project? Explain how it can be useful in controlling internet crimes in India.
Next question on this syllabus topic (2019 · Q10). View answer →
-
Is every WhatsApp cheat only an IT Act case?
Often it is IPC cheating plus IT Act sections. Charge-sheets should use both, not a ritual IT Act citation.
-
Can India arrest a foreign ransomware gang easily?
Attribution and extradition are slow. Resilience and payment-trail disruption matter as much as a wanted poster.
Same topic · past papers
UPSC has asked this before
These previous-year questions sit on the same topic. Open one to practise the earlier ask.
-
2021 · Q20 · GS III · 15 marks
Analyse the complexity and intensity of terrorism, its causes, linkages and obnoxious nexus. Also suggest measures required to be taken to eradicate the menace of terrorism. -
2015 · Q14 · GS III · 12 marks
India's Traditional Knowledge Digital Library (TKDL) which has a database containing formatted information on more than 2 million medicinal formulations is proving a powerful weapon in country's fight against erroneous patents. Discuss the pro and cons of making the database available publicly available under open source licensing. -
2025 · Q17 · GS III · 15 marks
Mineral resources are fundamental to the country's economy and these are exploited by mining. Why is mining considered an environmental hazard? Explain the remedial measures required to reduce the environmental hazard due to mining. -
2021 · Q19 · GS III · 15 marks
Analyse the multidimensıonal challenges posed by external state and non-state actors, to the internal security of India. Also discuss measures required to be taken to combat these threats.
More from this topic
Q20 · UPSC Mains 2026 · GS III · 15 marks · Solution
Discuss counterfeit currency and money laundering as major sources of terror funding in India. State the actions being taken at International level to check these menaces. Highlight the role of Financial Action Task Force (FATF) and methods of compliance by its member states in preventing terror funding.
Cyber Security and Money Laundering
• FICN funds networks and damages monetary trust. • Laundering uses placement–layering–integration, hawala and sometimes digital rails. • India: PMLA, UAPA finance provisions, FIU-IND, ED, NIA, RBI AML/KYC. • International: UN terror-finance conventions and sanctions lists. • FATF sets global AML/CFT standards via 40 Recommendations. • Members comply through laws, FIUs, KYC/STR duties, beneficial ownership, freezes. • Mutual evaluations judge both technical rules and real-world effectiveness. • Grey/black listing raises correspondent-banking and reputational costs.
Q9 · UPSC Mains 2026 · GS III · 10 marks · Solution
Explain how fake news and disinformation pose threat to Internal Security and Public Order in Indian context? In this regard, discuss salient features of amendments in respect of Information Technology (Intermediatory Guidelines and Digital Media Ethics Code) Rules 2021.
Cyber Security and Money Laundering
• Viral falsehoods can trigger communal violence and mob justice. • Disinformation aids radicalisation and confuses crisis response. • Elections and institutional trust are soft targets of coordinated lies. • IT Rules 2021 impose due diligence and grievance duties on intermediaries. • April 2023 amendment added government FCU flagging for Centre-related falsehoods. • PIB Fact Check Unit notified 20 March 2024 under the Rules. • Bombay HC (Sep 2024) struck down the FCU amendment as unconstitutional; further litigation ongoing. • Lasting response needs literacy, fast official facts, and proportionate law.
Q19 · UPSC Mains 2022 · GS III · 15 marks · Solution
What are the different elements of cyber security ? Keeping in view the challenges in cyber security, examine the extent to which India has successfully developed a comprehensive National Cyber Security Strategy.
Cyber Security and Money Laundering
Cyber security elements are confidentiality, integrity, availability, authentication, human process, supply chain, and legal institutions. India’s notified document is the National Cyber Security Policy 2013. A National Cyber Security Strategy was discussed around 2020; a complete public successor was not firmly in force as a single comprehensive charter by 2022. Operational bodies include CERT-In, NCIIPC and I4C, plus sector regulators. Gaps remain in MSME/hospital security, skills, supply chain and fragmented law.